Trusted by
WTHQ puts every NCA, SAMA and PDPL obligation, control and piece of evidence into one living record — with AI that runs entirely inside your own walls. So the next audit is an export, not a scramble.
Trusted by
A look inside WTHQ — governance, risk and compliance sharing one live record.
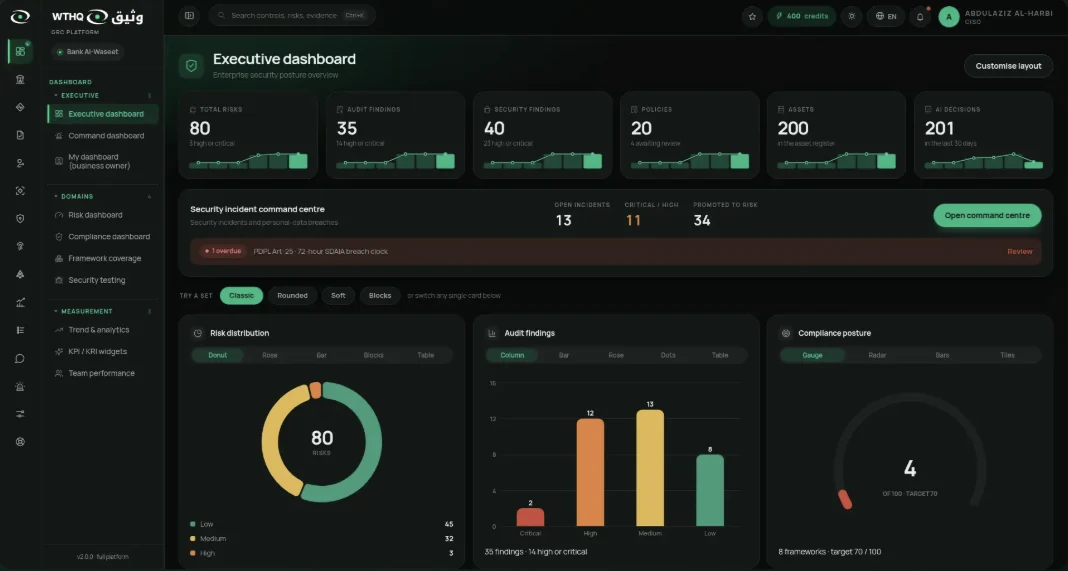
Risks, audit findings, policies and AI decisions in one view, with the incident command centre and the PDPL breach clock front and centre.
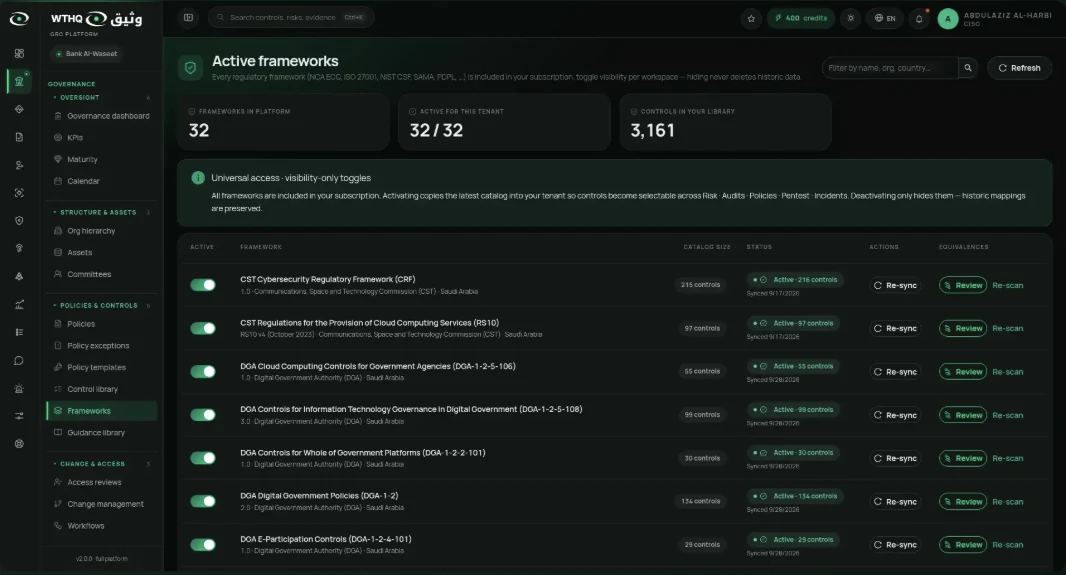
Saudi and international frameworks come pre-loaded — NCA, SAMA, CST, DGA, PDPL, ISO — with control counts, sync status and the equivalences between them.
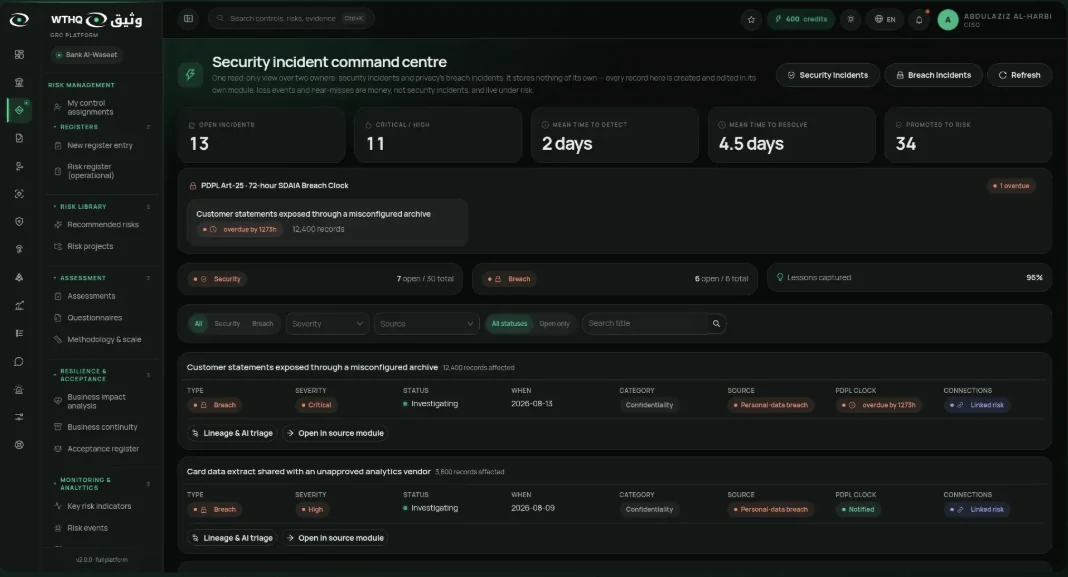
Security incidents and personal-data breaches side by side, with the PDPL 72-hour clock, time to detect and resolve, and links to the risks they create.
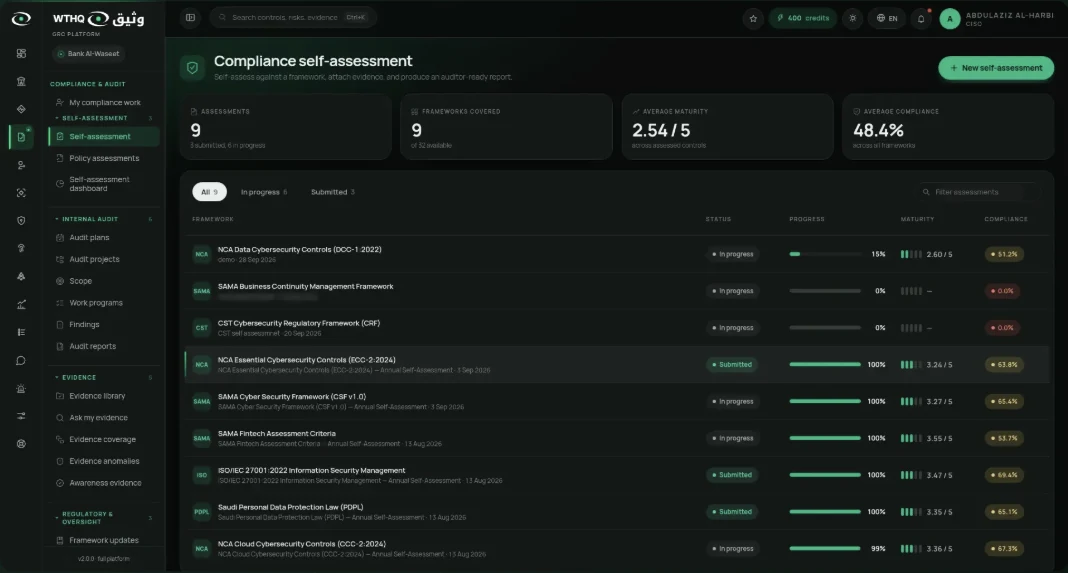
Assess against any framework, attach evidence, and follow progress, maturity and compliance per framework through to an auditor-ready report.
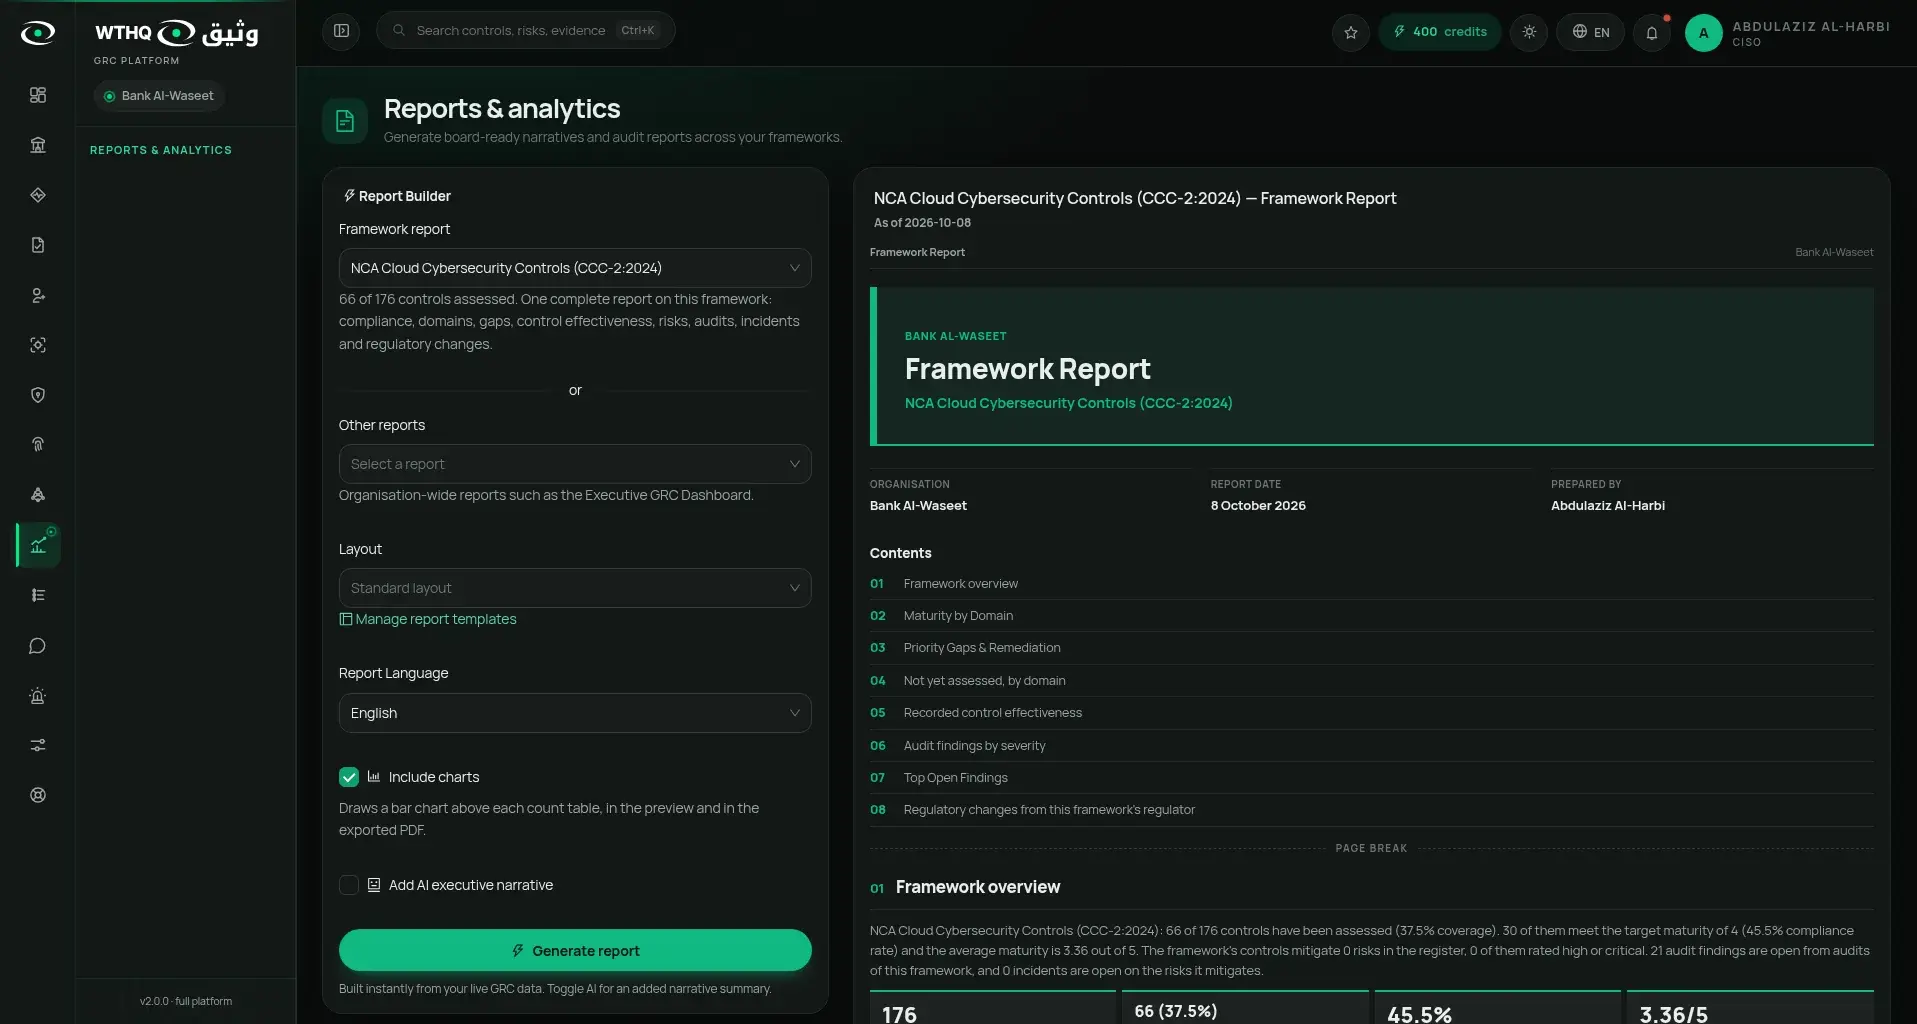
Pick a framework and get a report assembled from the controls, risks, findings and incidents already in your record — with charts and an optional AI executive narrative, ready to export as PDF.
Most GRC teams in the Kingdom are doing excellent work with tools that were never built for them. It shows up the same way every time: in the two weeks before an audit.
Policies in SharePoint, risks in Excel, vendor answers in email, incident notes with someone who left in March. Every audit starts with a hunt.
Western GRC suites treat NCA ECC and SAMA CSF as add-on libraries. Mappings drift, Arabic is an afterthought, and your team fills the gaps by hand.
Cloud LLMs can't touch regulated data, so the smartest tooling stays out of reach for exactly the teams who need it most.
WTHQ was built in the Kingdom, for the Kingdom's regulators, so that compliance becomes one record you can trust — not a project you repeat every year.
Three moves. After the third, audit season stops being a season.
32 KSA and international frameworks — over 3,000 controls — come pre-loaded and kept current. WTHQ's AI cross-maps controls between them, so one piece of evidence satisfies many obligations at once.
Policies, risks, vendors, incidents and training link to the controls they satisfy. Change one thing and see everything it touches.
Live posture per framework, a tamper-evident audit trail, and evidence packs generated on demand. Audit week becomes an export.
Every module writes to the same record, so a vendor finding, a policy change and an incident all show up against the control they affect.
Versioning, approvals, committees and multi-stage workflows, each policy mapped to the controls it enforces.
3×3 to 5×5 matrices, FAIR monetary quantification, KRIs, scenarios and emerging-risk alerts your board can act on.
Pre-loaded NCA, SAMA, PDPL, ISO and NIST. AI cross-mapping, maturity assessments and the full audit lifecycle in one place.
Vendors auto-tiered 1 to 4, tier-matched questionnaires, and an isolated supplier portal so nobody emails a spreadsheet again.
The PDPL 72-hour breach clock starts the moment you log it. Cross-module lineage and AI-drafted narratives keep the regulator informed on time.
Awareness training, phishing simulation and a behavioural risk index that turns your people from the weakest link into a measured control.
Most "AI-powered" GRC tools send your control evidence to a cloud model in another jurisdiction. For a SAMA-regulated bank or a government entity, that's not a feature. It's a finding.
WTHQ's models run on your own infrastructure, CPU or GPU, with zero external API calls and zero data egress. Every risk score comes with a SHAP-based explanation your auditors can read, in Arabic or English.
It's not a translated product. Arabic and right-to-left are native, so the regulator sees exactly what your team sees.
See the AI run locally in the demoHonest comparison. Spreadsheets are free and legacy suites are proven. Neither was built for the Kingdom's regulators or for AI you're allowed to use.
| Capability | Spreadsheets | Legacy GRC suites | WTHQ |
|---|---|---|---|
| NCA ECC, SAMA CSF, PDPL native | Manual | Add-on libraries | Pre-loaded and maintained |
| Arabic-first with true RTL | Depends on you | Translation layer | Native throughout |
| AI runs inside your network | No AI | Cloud inference | 100% on-premise, 0 egress |
| One evidence item satisfies many controls | Copy-paste | Manual mapping | AI cross-mapping across 32 frameworks |
| PDPL 72-hour breach clock | Calendar reminder | Generic SLA timers | Built-in, with regulator narrative |
| Tamper-evident audit trail | Version history | Standard logs | Hash-chained, provable |
| Explainable risk scores | Your formulas | Black box | SHAP-based, auditor-readable |
Your information security team will have questions before your compliance team gets a login. WTHQ was designed with those questions in mind.
Multi-tenant by design with database-enforced separation between entities.
Every change is linked to the last. Tampering is mathematically evident.
Active Directory and SSO integration, MFA and WebAuthn passkeys out of the box.
Sensitive fields encrypted individually, not just at the disk.
Exports carry invisible watermarks so leaked documents are traceable.
Restrict access to known networks, including the supplier portal.
Straight answers. If yours isn't here, bring it to the demo and we'll answer it live.
No. Models, database and application all run inside your infrastructure. There are zero external API calls and zero data egress. WTHQ can run fully air-gapped.
No. WTHQ runs on CPU-only servers. GPUs make cross-mapping and narrative drafting faster but are not required.
Fully supported. The interface, reports, framework text and AI output are natively bilingual with true right-to-left layout. Nothing is machine-translated after the fact.
Updated frameworks arrive as versioned packages. The AI proposes new mappings from your existing evidence, your team reviews and approves, and the change is recorded in the audit trail.
Yes. Suppliers answer tier-matched questionnaires in an isolated portal. They see only their own questionnaire and nothing about your internal record.
It depends on your infrastructure and how much existing evidence you want migrated. We scope a pilot with you on the first call and give you a dated plan before you commit to anything.
Thirty minutes, on your frameworks, with your sector's controls. No slides about the cloud. Just the platform running where your data would live.
We'll be in touch within one business day to schedule your demo.